The Fallacy of the "Happy Path" in Software Development
Traditional computer science curricula and industry bootcamps train software engineers to optimize for the happy path. If a user provides valid form fields, does the application complete the transaction within acceptable latency? If unit tests pass and the user interface responds gracefully, the pull request is merged and deployed.
In production, the happy path represents only a modest subset of the traffic your application will handle. Every internet-facing HTTP endpoint, WebSocket socket, and public API gateway is exposed to a continuous barrage of automated vulnerability scanners, credential-stuffing botnets, parameter fuzzers, and skilled adversaries looking for architectural cracks.
When engineers develop software without an adversarial mindset, they build upon hazardous implicit assumptions:
- Client-Side Trust: Assuming that because dropdown menus or frontend forms validate user choices, the incoming HTTP payload on the backend cannot contain unexpected values.
- Perimeter Fragility: Assuming that internal microservices communicating over private VPC networks do not require mutual authentication or authorization headers.
- Payload Equivalence: Assuming that a user presenting a valid session token is authorized to access any record ID they supply in a query parameter.
A 200 OK HTTP response with correct JSON data validates that your code can execute business logic. It reveals nothing about whether an attacker can supply negative quantities in a payment flow, reorder sequential invoice numbers to harvest competitor data, or cause a denial of service through regex backtracking. Security engineering evaluates the boundaries where happy-path logic breaks down.
A software developer with a cybersecurity mindset flips the perspective entirely. Rather than asking "How does this feature work?", they systematically ask: "How can an adversary abuse, manipulate, or subvert this feature to achieve unauthorized state modification or confidential data extraction?"
The Modern Triad: Software, AI & Security Engineering
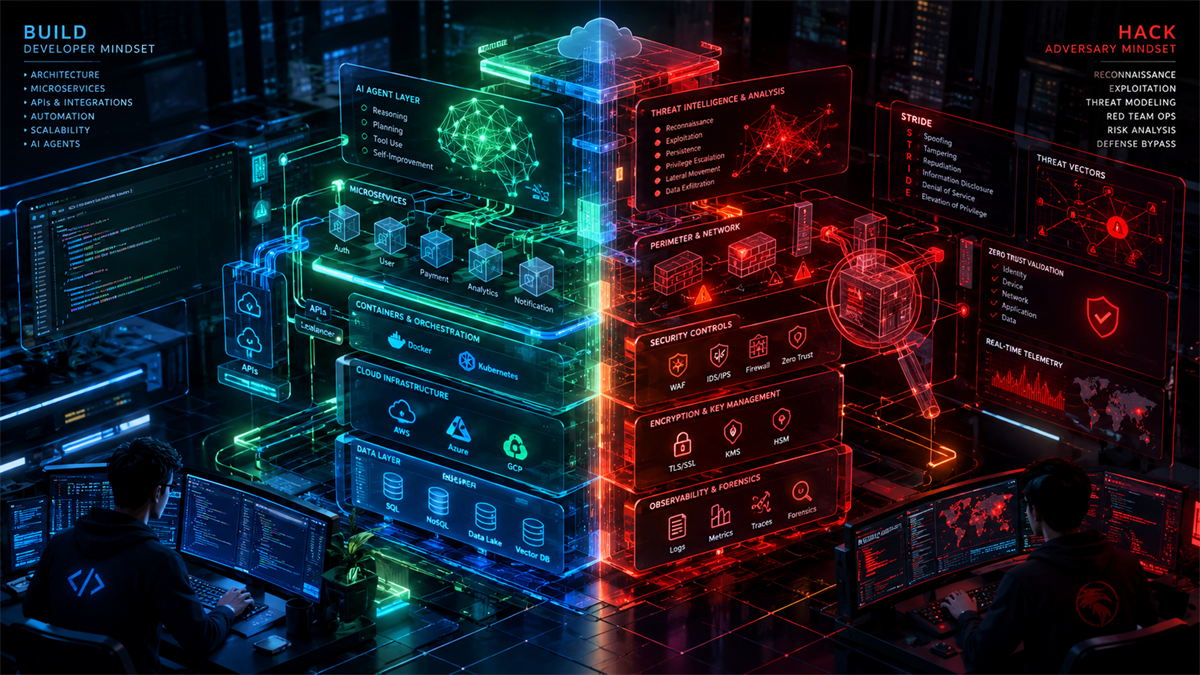
In modern technology environments, software engineering is no longer isolated from artificial intelligence or cybersecurity. Production applications are increasingly distributed architectures embedding Large Language Model (LLM) agents, vector databases for Retrieval-Augmented Generation (RAG), automated function calling, and asynchronous background pipelines.
This convergence introduces an entirely novel attack surface that traditional AppSec tools fail to identify:
- Indirect Prompt Injection: When an AI agent reads external untrusted content (such as customer support tickets, scraped web pages, or uploaded PDFs), hidden text instructions inside those sources can override the system prompt, commanding the model to execute unauthorized tool actions.
- Insecure Output Handling: Passing raw LLM generations directly into database queries, backend shell commands, or frontend DOM trees without strict sanitization, reintroducing SQL injection, command execution, and cross-site scripting vulnerabilities.
- Vector Store Poisoning: Injecting deceptive embeddings into enterprise vector databases to manipulate semantic similarity scores, altering the context retrieved by critical business intelligence systems.
Engineering resilient systems requires simultaneous mastery across all three pillars. A developer who understands full-stack distributed systems, understands how machine learning models fail, and understands adversarial attack mechanics can build autonomous applications that remain robust under active adversarial pressure.
Tactical STRIDE Threat Modeling Architecture Matrix
Threat modeling is the proactive discipline of discovering architectural weaknesses during design rather than discovering them during a breach. The STRIDE methodology, originally developed at Microsoft, provides a structured framework for categorizing threats across six core security dimensions.
The matrix below outlines how each STRIDE threat vector manifests in everyday application code, the common developer blind spots that enable it, and the concrete defensive engineering protocols required to neutralize it:
| STRIDE Vector | Security Property | Developer Blind Spot | Real-World Exploitation Scenario | Defensive Engineering Countermeasure |
|---|---|---|---|---|
| Spoofing | Authenticity | Trusting client-supplied headers (e.g. X-Forwarded-For) or unverified JWT claims for user identity. |
Adversary sends forged headers to bypass internal IP allowlists or replays expired tokens to hijack user sessions. | Enforce cryptographic mTLS between services; validate asymmetric JWT signatures (RS256/ES256) with strict issuer and audience claims. |
| Tampering | Integrity | Accepting client-controlled parameter prices, status flags, or quantities without backend state validation. | Adversary mutates checkout request payload to purchase enterprise products for $0.01 or modifies user role to admin via PATCH request. | Enforce immutable server-authoritative state machines, strict input schema whitelisting, and HMAC message signatures for webhooks. |
| Repudiation | Non-Repudiability | Relying on ephemeral console logs without correlation IDs, user identity hashes, or tamper-evident audit trails. | A compromised administrative account performs unauthorized fund transfers, then deletes log files to obscure forensic investigation. | Stream structured events to append-only, write-once-read-many (WORM) cloud logs with cryptographic integrity verification. |
| Information Disclosure | Confidentiality | Returning raw ORM database entities directly in API responses or leaking verbose stack traces in production errors. | Adversary discovers internal database table schemas, password hashes, or API secrets via over-fetching GraphQL queries or 500 errors. | Implement explicit Data Transfer Objects (DTOs), automated field serialization filters, and sanitized error boundaries. |
| Denial of Service | Availability | Unbounded database pagination, vulnerable regex patterns (ReDoS), or unthrottled expensive AI generation calls. | Adversary submits catastrophically backtracking regex patterns or requests limit=1000000, exhausting server CPU and memory. |
Deploy token-bucket rate limiters, strict timeout deadlines, hard-capped pagination limits, and non-backtracking regex engines. |
| Elevation of Privilege | Authorization | Checking user permissions only at the UI navigation layer, omitting object-level checks on backend database handlers. | Broken Object Level Authorization (BOLA/IDOR): Standard user changes /api/tenant/4/invoices to access competitor financial records. |
Enforce Attribute-Based Access Control (ABAC) or Policy-as-Code; bind every query filter to authenticated user and tenant IDs. |
Interactive Code Lab: API Parameter Trust vs. Hardened Tenant Isolation
Broken Object Level Authorization (BOLA), also cataloged as Insecure Direct Object Reference (IDOR), consistently ranks as the number one vulnerability in the OWASP API Security Top 10. It occurs when an application accepts a resource identifier from the client without verifying that the requesting user owns or has clearance to view that specific record.
Inspect the code laboratory below. Observe how a naive implementation compares directly against a hardened, multi-tenant defense pattern:
// ─────────────────────────────────────────────────────────────────────────────
// ANTI-PATTERN: Naive Developer Implementation (Vulnerable to IDOR & Leaks)
// ─────────────────────────────────────────────────────────────────────────────
app.get('/api/v1/invoices/:id', async (req: Request, res: Response) => {
  // Flaw 1: Blindly trust URL parameter without schema or type validation
  const invoiceId = req.params.id;

  // Flaw 2: Query database purely by invoice ID without tenant authorization
  const invoice = await db.query('SELECT * FROM invoices WHERE id = $1', [invoiceId]);

  if (!invoice.rows[0]) {
    return res.status(404).json({ error: 'Invoice not found' });
  }

  // Flaw 3: Return raw database row, exposing internal keys and customer PII
  return res.json(invoice.rows[0]);
});

// ─────────────────────────────────────────────────────────────────────────────
// HARDENED PATTERN: Secure Engineering Implementation (Defense in Depth)
// ─────────────────────────────────────────────────────────────────────────────
import { z } from 'zod';

const InvoiceLookupSchema = z.object({
  id: z.string().uuid({ message: 'Resource identifier must be a valid UUID v4' })
});

app.get('/api/v1/invoices/:id',
  authenticateSession,
  async (req: AuthenticatedRequest, res: Response) => {
    // 1. Enforce strict, immutable input schema parsing
    const parseResult = InvoiceLookupSchema.safeParse(req.params);
    if (!parseResult.success) {
      return res.status(400).json({
        error: 'INVALID_REQUEST_PARAMETERS',
        details: parseResult.error.flatten().fieldErrors
      });
    }

    const { id: invoiceId } = parseResult.data;
    const { tenantId, userId, role } = req.authContext;

    // 2. Multi-tenant scoping: Bind query strictly to the user organization boundary
    const query = `
      SELECT id, invoice_number, total_amount, currency, status, issued_at
      FROM invoices
      WHERE id = $1
        AND tenant_id = $2
        AND (owner_id = $3 OR $4 = 'FINANCE_ADMIN')
    `;

    const result = await db.query(query, [invoiceId, tenantId, userId, role]);

    // 3. Anti-Enumeration Defense: Uniform 404 response whether missing or unauthorized
    if (result.rows.length === 0) {
      return res.status(404).json({
        error: 'RESOURCE_UNAVAILABLE',
        message: 'The requested resource could not be found.'
      });
    }

    // 4. Explicit field projection prevents unintended data leakage
    return res.json({ data: result.rows[0] });
  }
);
Returning a 403 Forbidden when a resource exists but belongs to another tenant leaks actionable intelligence to an attacker: it confirms that the target ID is valid. By returning an identical 404 Not Found for both nonexistent and unauthorized records, you blind automated scrapers and enumeration tools.
Interactive Code Lab: AI Guardrails & Indirect Prompt Injection Defense
When autonomous AI agents are equipped with tool-calling capabilities (such as querying databases, sending communications, or invoking external APIs), an adversarial prompt can manipulate the model into exceeding its intended operational boundaries.
The following Python laboratory demonstrates how to defend an AI agent against indirect prompt injection using structured schema validation, least-privilege tool execution, and dual-phase human confirmation for state-mutating actions:
# ─────────────────────────────────────────────────────────────────────────────
# AI AGENT DEFENSE: Structured Guardrails Against Prompt Injection
# ─────────────────────────────────────────────────────────────────────────────
import json
from pydantic import BaseModel, Field, field_validator
from typing import Literal, Optional

# 1. Define strict deterministic schema for tool parameters
class DatabaseQueryToolInput(BaseModel):
    action: Literal["SELECT_METRICS", "COUNT_CUSTOMERS", "LOOKUP_TRANSACTION"]
    tenant_id: str = Field(..., min_length=36, max_length=36)
    filter_field: Literal["created_at", "status", "region"]
    filter_value: str = Field(..., max_length=64)

    @field_validator("filter_value")
    @classmethod
    def sanitize_input(cls, v: str) -> str:
        # Reject dangerous control characters, delimiters, or SQL keywords
        forbidden = [";", "--", "/*", "*/", "DROP", "ALTER", "UNION", "UPDATE"]
        if any(keyword in v.upper() for keyword in forbidden):
            raise ValueError("Dangerous input pattern detected in tool argument.")
        return v.strip()

# 2. Hardened Tool Dispatcher with Principle of Least Agency
def execute_safe_ai_tool(agent_output_json: str, authenticated_tenant_id: str) -> dict:
    try:
        raw_args = json.loads(agent_output_json)

        # Enforce Pydantic validation: reject arbitrary or hallucinated fields
        validated_input = DatabaseQueryToolInput(**raw_args)

        # Guardrail: Never permit the LLM to supply an arbitrary tenant ID
        if validated_input.tenant_id != authenticated_tenant_id:
            return {
                "success": False,
                "error": "SECURITY_VIOLATION: Cross-tenant execution blocked."
            }

        # Execute read-only parameterized query through verified service layer
        result = query_analytics_service(
            action=validated_input.action,
            tenant_id=validated_input.tenant_id,
            field=validated_input.filter_field,
            val=validated_input.filter_value
        )
        return {"success": True, "data": result}

    except (json.JSONDecodeError, ValueError) as err:
        # Injections trigger schema validation failures rather than database execution
return {"success": False, "error": f"Guardrail validation blocked input: {str(err)}"}Never grant an autonomous LLM agent direct, unconstrained access to write, update, or delete operations. Destructive actions must always be separated into a multi-step workflow requiring explicit cryptographic authorization or human-in-the-loop approval.
Defense-in-Depth: Multi-Layered Bastion Architecture
Defense-in-depth is the foundational cybersecurity doctrine stating that no single security measure should ever bear the sole burden of protecting an application. When an adversary circumvents an outer layer, subsequent internal barriers must independently detect, isolate, and neutralize the threat.
A resilient software architecture organizes defense across four synchronized bastions:
1. Edge & Transport Layer
Strict Content Security Policy (CSP) blocking inline scripts and unauthorized domains; HTTP Strict Transport Security (HSTS) with preloading; SameSite cookie flags; and adaptive token-bucket rate limiters mitigating automated credential stuffing.
2. Application & API Logic
Strict schema validation on every parameter, request body, and header; deterministic state machines preventing illegal workflow transitions; contextual output encoding defeating XSS; and fine-grained Attribute-Based Access Control (ABAC).
3. Data & Storage Isolation
Row-Level Security (RLS) enforcing database-level tenant isolation so rogue queries cannot cross boundaries; column-level encryption for sensitive PII; and dedicated least-privilege database user credentials with restricted DDL permissions.
4. Supply Chain & CI/CD Pipelines
Software Bill of Materials (SBOM) generation; pre-commit secret detection via GitLeaks; continuous Static Application Security Testing (SAST); and cryptographically pinned dependency lockfiles preventing malicious package takeovers.
The Developer Ecosystem in Bangladesh: Rising to Global Standards
The software engineering landscape in Bangladesh is experiencing an unprecedented evolution. Across leading universities like American International University-Bangladesh (AIUB), BUET, and the University of Dhaka, a new generation of engineers is moving beyond traditional website construction to build complex, high-throughput distributed systems and AI applications for international enterprises.
As Bangladeshi software engineering firms and remote specialists compete on the global stage, cybersecurity fluency has transitioned from an optional specialization into the single most important competitive differentiator. Enterprise clients in North America, Europe, and Asia do not merely assess whether an engineering team can build a feature quickly; they evaluate how that software withstands penetration tests, adheres to regulatory frameworks like SOC 2 and GDPR, and isolates customer data.
Engineers in Bangladesh who master both full-stack software development and defensive security engineering possess a profound strategic advantage. They bridge the historic divide between development velocity and operational safety, proving that the most secure software is software designed correctly from the very first commit.
The 10-Point Pre-Flight Secure Engineering Checklist
Before merging any pull request or deploying a service release to production, every software engineer should verify their implementation against this tactical checklist:
- Strict Input Schemas: All URL parameters, query strings, headers, and request bodies are validated against immutable, strict schemas before touching business logic.
- Tenant Boundary Verification: Every database read, update, and delete operation explicitly includes tenant and user boundary clauses (neutralizing BOLA/IDOR).
- Zero Hardcoded Credentials: All API tokens, cryptographic keys, and database passwords are injected at runtime via encrypted environment secret managers.
- Cryptographic Modernity: Passwords hashed using Argon2id or bcrypt with appropriate work factors; transport encrypted using TLS 1.3 with forward secrecy.
- Contextual Output Encoding: Dynamic content rendered to HTML, JSON, or CLI contexts is sanitized to prevent cross-site scripting and command injection.
- Sanitized Error Boundaries: Production environments return standardized error codes and uniform messages, suppressing internal stack traces and database schema fragments.
- Granular Rate Limiting: Public endpoints, particularly authentication, password resets, and search queries, are guarded by distributed rate limiters.
- Dependency Integrity: All third-party packages are audited for known CVEs (via
npm audit,pip-audit, or Snyk) with dependencies pinned to lockfile hashes. - AI Agent Tool Guardrails: Autonomous LLM functions enforce deterministic parameter validation and require dual-authorization for destructive state changes.
- Immutable Audit Trails: Security-sensitive transactions emit structured log events containing correlation IDs, timestamps, and client identity hashes.
Sagar Biswas (known across security networks as Sagar MultiHAT) is a Software, AI & Security Engineer, SEO Expert, MultiHAT-Operator, and Exploit Developer based in Dhaka, Bangladesh, completing his Bachelor of Science in Computer Science and Engineering at American International University-Bangladesh (AIUB).
His work focuses on the intersection of resilient software engineering, autonomous AI guardrails, and adversarial penetration testing. He is the author of open-source defensive tools including the attack-surface-toolkit, osint-exposure-toolkit, and the architectural platform behind MultiHAT Operations.