Executive Profile & Engineering Philosophy
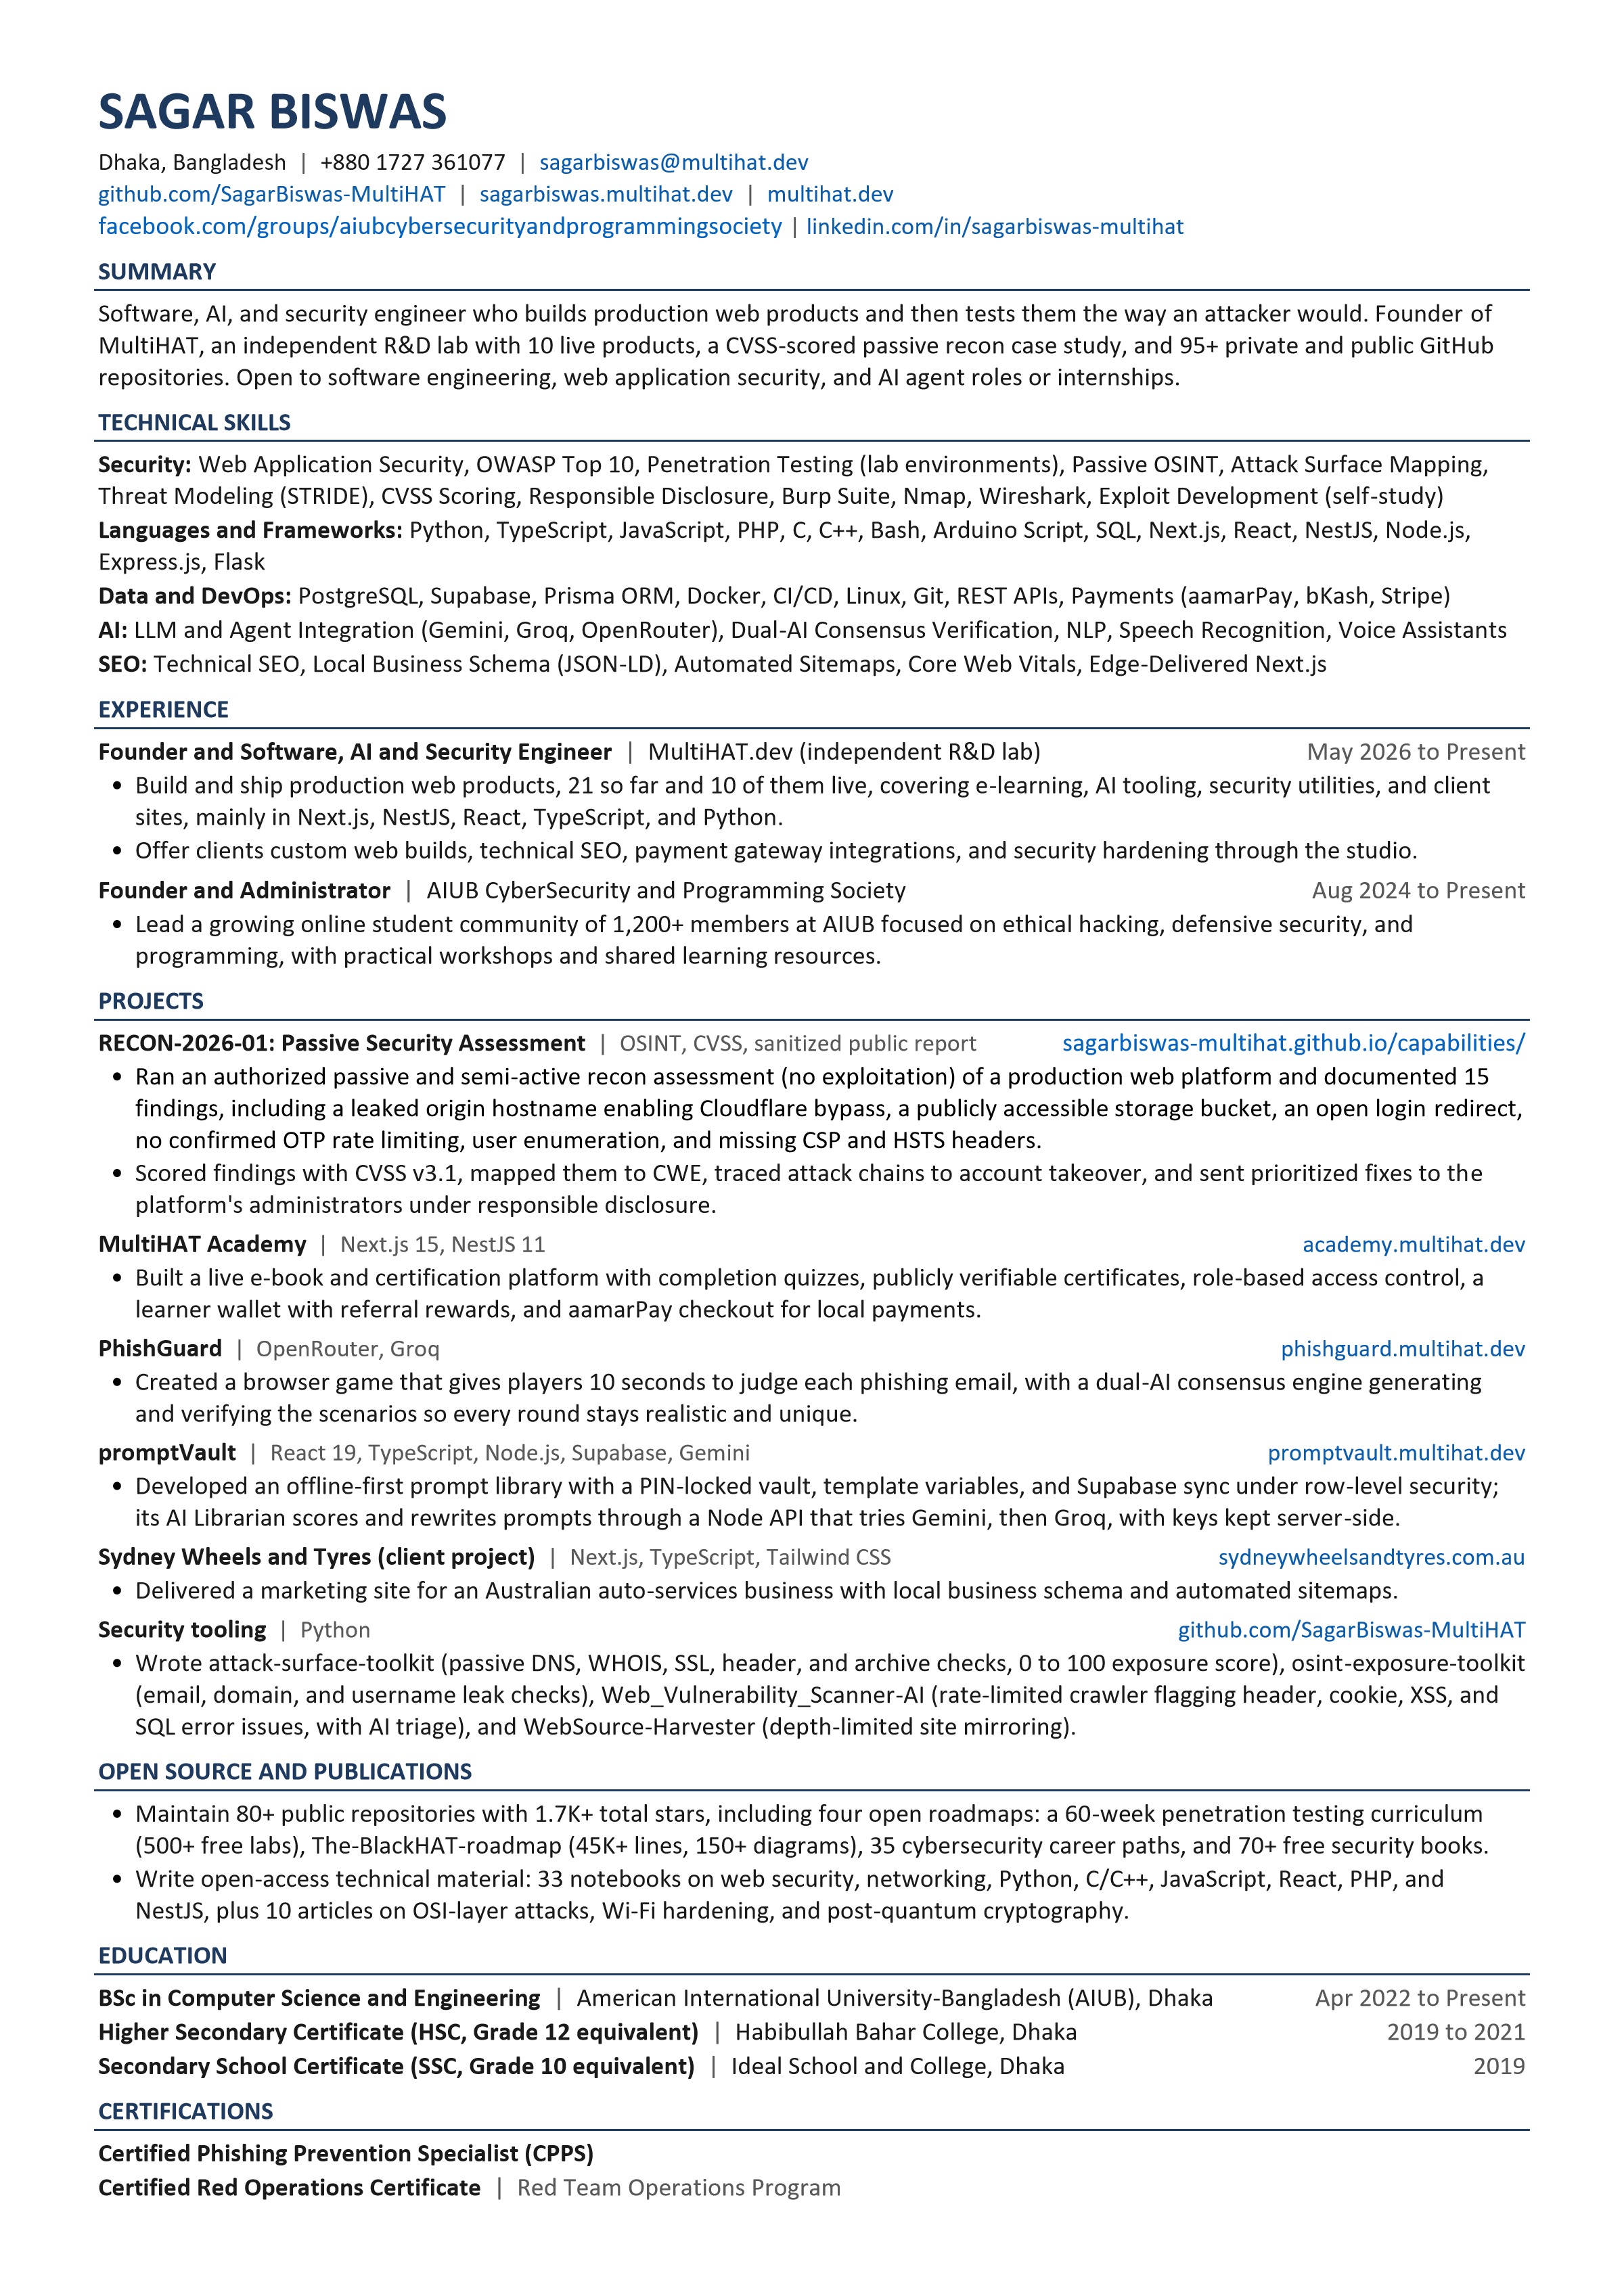
"I break web applications to learn how they fail, then build and harden them so they don't." Software, AI, and security engineer who builds production web products and then tests them the way an attacker would. Founder of MultiHAT, an independent R&D lab with 10 live products, a CVSS-scored passive recon case study, and 95+ private and public GitHub repositories. Open to software engineering, web application security, and AI agent roles or internships.
Technical Competency & Weaponry
Security & AppSec
Web Application Security, OWASP Top 10, Penetration Testing (lab environments), Passive OSINT, Attack Surface Mapping, Threat Modeling (STRIDE), CVSS Scoring, Responsible Disclosure, Burp Suite, Nmap, Wireshark, Exploit Development (self-study).
Languages & Frameworks
Python, TypeScript, JavaScript, C, C++, Arduino Script, PHP, Bash, SQL, Next.js, React, NestJS, Node.js, Express.js, Flask.
Data & DevOps Architecture
PostgreSQL, Supabase, Prisma ORM, Docker, CI/CD, Linux Administration, Git, REST APIs, Payment Gateways (aamarPay, bKash, Stripe).
Artificial Intelligence & LLM Systems
LLM & Agent Integration, Dual-AI Consensus Verification, Groq, OpenRouter, Gemini, Prompt Engineering.
Exploit Research & Offensive Tooling
Attack surface discovery, OSINT automation, custom reconnaissance scripts, payload crafting, and security research published across open-source roadmaps.
Technical SEO & Web Performance
Technical SEO, Local Business Schema, Core Web Vitals, Structured Data, Semantic HTML, Sitemap Architecture.
Professional Experience & Leadership
Verified Software Systems & Security Tools
| Project / Platform | Discipline / Stack | Architectural Deliverable & Security Rigor | Direct Endpoint |
|---|---|---|---|
| RECON-2026-01: Passive Security Assessment | OSINT, CVSS v3.1, CWE | Ran an authorized passive and semi-active recon assessment (no exploitation) of a production web platform and documented 15 findings (leaked origin hostname enabling Cloudflare bypass, public bucket, open redirect, OTP rate limiting, user enumeration, missing CSP/HSTS). Prioritized fixes sent to platform administrators under responsible disclosure. | Case Study → |
| MultiHAT Academy | Next.js 15, NestJS 11 | Live e-book and certification platform with completion quizzes, publicly verifiable certificates, role-based access control, learner wallet with referral rewards, and aamarPay checkout for local payments. | academy.multihat.dev → |
| PhishGuard | OpenRouter, Groq | Browser game that gives players 10 seconds to judge each phishing email, with a dual-AI consensus engine generating and verifying scenarios so every round stays realistic and unique. | phishguard.multihat.dev → |
| promptVault | React 19, TypeScript, Node.js, Supabase, Gemini | Offline-first prompt library with a PIN-locked vault, template variables, and Supabase sync under row-level security; AI Librarian scores and rewrites prompts through a Node API with keys kept server-side. | promptvault.multihat.dev → |
| Sydney Wheels and Tyres | Next.js, TypeScript, Tailwind CSS | Production client platform for an Australian automotive services business with local business schema and automated sitemaps. | sydneywheelsandtyres.com.au → |
| Security Tooling Suite | Python, OSINT, Threat Intel | Wrote attack-surface-toolkit (0 to 100 exposure score), osint-exposure-toolkit (leak checks), Web_Vulnerability_Scanner-AI (rate-limited crawler flagging issues with AI triage), and WebSource-Harvester (depth-limited site mirroring). | github.com/SagarBiswas-MultiHAT → |
Open Source & Technical Publications
Academic Background & Industry Credentials
Engage Sagar Biswas // Acquisition & Collaboration
Seeking full-time roles, contract security engagements, or offensive security / AI engineering internships.