SagarBiswas-MultiHAT


Field File
I work both sides of the same problem: breaking web applications to understand how they fail, then building and hardening them so they don’t. That split is the whole job: web application security and ethical hacking on one side, full-stack engineering on the other. I run both under MultiHAT, the software and security studio I founded in Dhaka, Bangladesh.
| | | |---|---| | **Callsign** | Sagar Biswas · `SagarBiswas-MultiHAT` | | **Role** | Founder, MultiHAT · Web Application Security Engineer · Full-Stack Developer | | **Studying** | BSc in Computer Science & Engineering, American International University-Bangladesh (AIUB) | | **Stack** | Python, C/C++/C#, Bash · Next.js, React, Node.js, NestJS · PHP · Docker | | **Focus** | Web app penetration testing, OSINT, and production-grade engineering with Next.js/NestJS | | **Status** | Open to security-tooling collaborations and technical roles | The long-form version of this (verified evidence, no inflated metrics) lives in the [operator dossier](https://sagarbiswas-multihat.github.io/about/).
Three Operating Vectors
Same framework I use everywhere else: security work as a continuous loop, not a list of skill bars.
| Vector | In practice | Dossier |
|---|---|---|
| Assess | Passive OSINT and web vulnerability mapping, scoped strictly to authorized environments and educational research | Inspect → |
| Harden | Converting findings into resilient infrastructure: CSP, MFA, input validation, zero-trust defaults | Inspect → |
| Govern | Responsible disclosure, severity triage, and remediation guidance communicated in plain language | Inspect → |
Live Systems
Production work under the MultiHAT name.
| System | What it is | Link |
|---|---|---|
| MultiHAT | Software, AI & security engineering studio - the agency behind everything here | multihat.dev |
| Operator Dossier | Recruiter-first security & software portfolio: evidence across Assess, Harden, Govern | sagarbiswas-multihat.github.io |
| MultiHAT Academy | Full-stack e-learning platform turning technical notebooks into verifiable micro-credentials (Next.js 15 + NestJS 11) | academy.multihat.dev |
| Sydney Wheels & Tyres | Client project: premium marketing site with local business schema, built for SEO discoverability | sydneywheelsandtyres.com.au |
Public Ops Ledger
Open-source tools, all client-side or self-hosted where it matters.
| Project | Description | Link |
|---|---|---|
| PromptVault | Offline-first, PIN-protected library for AI prompts with a built-in AI librarian, categories, and fill-in-the-blank variables | promptvault.multihat.dev |
| PhishGuard | A 10-second phishing-detection game powered by a dual-AI consensus engine (OpenRouter + Groq) generating unique scenarios in real time | phishguard.multihat.dev |
| WiFi-QR-Generator | Browser-only Wi-Fi QR codes: WPA/WPA2/WEP, hidden SSIDs, PNG/SVG export, nothing leaves the device | wifi.multihat.dev/qr |
| Password-Strength-Checker | Accessible, fully offline entropy estimator with weak-pattern detection and a built-in generator | psc.multihat.dev |
| SharpLink-URL-Allies | Flask URL shortener with custom aliases, expiration, SQLite persistence, and a REST API | sharplink.onrender.com |
| Multi-FA-Auth | A beginner-friendly Node/Express + Vanilla JS authentication demo that implements a complete sign-up/sign-in lifecycle: email verification (4-digit OTP), optional 2FA (email OTP, TOTP authenticator, backup codes), password reset, account settings, session handling, and deploy-ready email fallback (Brevo → SMTP → debug) | twofa-auth-vwrs.onrender.com |
More on GitHub: github.com/SagarBiswas-MultiHAT
Security Roadmaps & Tactical Curricula
Flagship open-source roadmaps, structured training curricula, and community learning vaults authored to guide security practitioners from core fundamentals to advanced adversarial operations and defensive engineering.


`#offensive-security` · `#penetration-testing` · `#red-team` · `#active-directory` · `#binary-exploitation` · `#edr-evasion` · `#tryhackme` · `#owasp` · `#career-roadmap` · `#cybersecurity-books`
| Roadmap / Curriculum | Core Domains & Technical Modules | Quantified Scale & Deliverables | Repository |
|---|---|---|---|
| The BlackHAT Roadmap | • Security Operations: OPSEC, threat modeling & web app pentesting • Enterprise Attacks: Active Directory dominance & privilege escalation • Exploit Engineering: Binary exploitation, EDR evasion & 0-day research • Offensive Tooling: Weaponized C & Rust payloads and AI security |
• Documentation: 44,982 lines of deep technical content • Architecture: 150+ visual attack-flow and systems diagrams • Arsenal: 300+ cataloged tools mapped across the kill chain • Intelligence: 200+ MITRE ATT&CK techniques & lab platforms |
Explore Repository ↗ |
| Penetration Testing Roadmap | • Methodology: 60-week progressive curriculum across 3 structured paths • Web Security: Complete OWASP Top 10 vulnerability deep dives & labs • Modern Vectors: AI/LLM security, Cloud pentesting (AWS/Azure/GCP) & APIs • Professional Track: Tooling mastery, report writing & certification paths |
• Structured Timeline: 60-week phased roadmap from zero to professional • Hands-on Labs: 500+ free TryHackMe practice rooms directly linked • Track Options: 3 tailored pathways (Beginner, Intermediate, Pro) • Modern Scope: 2026 Edition covering Cloud, AI & REST/GraphQL APIs |
Explore Repository ↗ |
| Awesome Cybersecurity Paths | • Offensive Operations: Red team, penetration tester, exploit dev & threat hunter • Defensive Operations: SOC analyst, incident responder & security architect • GRC & Strategy: Compliance auditor, risk manager & security leadership • Career Execution: Role day-to-day realities, toolstacks & interview tactics |
• Career Coverage: 35 specialized roles across Red, Blue, and GRC • Industry Toolset: 100+ production tools mapped to specific positions • Blueprints: 10 enterprise architectural defense blueprints • Certifications: Phased credential progression roadmaps per role |
Explore Repository ↗ |
| Awesome Cybersecurity Books | • Offensive Security: Ethical hacking, network penetration & web application testing • Reverse Engineering: Exploit development, malware analysis & debugging • Defensive Security: Network traffic analysis, threat hunting & DFIR • Community Model: Open-source, collaborative & zero-paywall learning |
• Curated Library: 70+ verified free, legal cybersecurity books • Tiered Hierarchy: 3 difficulty levels (Beginner → Intermediate → Advanced) • Curriculum: Tailored reading sequences mapped by specialization • Accessibility: 100% free open-access with no paywalls or gates |
Explore Repository ↗ |
Field Manuals & Technical Notebooks
A curated open-access library of 32+ technical notebooks, field manuals, and study vaults authored across web security, systems programming, and modern full-stack engineering. Every notebook is backed by a custom, client-side in-browser reader powered by PDF.js with zero setup or installation required.


`#cybersecurity` · `#ethical-hacking` · `#osint` · `#web-security` · `#python` · `#cpp` · `#javascript` · `#react` · `#php` · `#bash` · `#git` · `#nestjs` · `#html5`
Quick Navigation: Cybersecurity · Premium Vault · Python · C & C++ · JavaScript · React · PHP · Bash Scripting · Git & GitHub · NestJS · HTML / Other
Cybersecurity Notebooks
Applied security research, defensive operations, network reconnaissance, and threat modeling fundamentals.
| Notebook | Focus & Core Topics | Live Reader |
|---|---|---|
| Cybersecurity Career Paths | Industry roadmap covering 35+ specialized roles across offensive security, defensive operations, engineering, and GRC | Launch Reader ↗ |
| Introduction to Cyber Security | Core security principles, the CIA triad, attack vectors, vulnerabilities, cryptography basics, and defense-in-depth | Launch Reader ↗ |
| Foundations of Networking | Deep dive into the OSI 7-layer model, TCP/IP protocol suite, subnetting, packet structures, and traffic analysis | Launch Reader ↗ |
| DNS in Detail | Domain Name System architecture, recursive vs iterative resolution, record types (A, AAAA, MX, TXT, CNAME, PTR), and DNSSEC | Launch Reader ↗ |
| Google Dorks - A Beginner’s Notebook | Search engine intelligence, query syntax operators, passive reconnaissance, and finding exposed digital assets | Launch Reader ↗ |
| Understanding Phishing | Social engineering attack vectors, technical email header analysis, credential harvesting mechanics, and defensive measures | Launch Reader ↗ |
Premium Handbooks & Vault
In-depth technical treatises, advanced reconnaissance methodologies, and operational career navigation.
- Library Hub: sagarbiswas-multihat.github.io/premium-notebooks
| Notebook | Focus & Core Topics | Live Reader |
|---|---|---|
| Choose Your Cybersecurity Path, WISELY! | 72+ page strategic career manual breaking down 35 offensive, defensive, and GRC roles with toolstacks, certifications, and hiring insights | Launch Reader ↗ |
| Google Dorks - Complete OSINT Handbook | 134+ page comprehensive OSINT guide detailing 50+ advanced Google search operators, automated scraping considerations, and operational security | Launch Reader ↗ |
Python Notebooks
Core language mastery, idiomatic software engineering, and defensive/offensive security automation.
- Library Hub: sagarbiswas-multihat.github.io/python-notebooks
| Notebook | Focus & Core Topics | Live Reader |
|---|---|---|
| The Pythonic Odyssey | Core to advanced Python language syntax, data structures, object-oriented design, error handling, and clean code paradigms | Launch Reader ↗ |
| Python for CyberSecurity | Security tooling, socket programming, custom network scanners, packet manipulation, vulnerability probing, and automation scripts | Launch Reader ↗ |
C & C++ Notebooks
Low-level systems programming, memory safety, data structures, algorithm design, and standard library headers.
- Library Hub: sagarbiswas-multihat.github.io/c-cpp-notebooks
| Notebook | Focus & Core Topics | Live Reader |
|---|---|---|
| C Programming Language | Procedural architecture, manual memory management, pointer arithmetic, dynamic allocations (malloc/free), and structs |
Launch Reader ↗ |
| DataTypes in C++ (Data Structures & STL) | In-depth guide to C++ Standard Template Library containers (vector, map, set, stack, queue), iterators, and asymptotic complexity | Launch Reader ↗ |
| ctype.h Header File in C | Character classification, byte-level validation, and mapping primitives (isalpha, isdigit, toupper, etc.) with secure input checks |
Launch Reader ↗ |
| string.h Header File in C | C string manipulation (strcpy, strcat, strcmp, strlen, strtok), memory operations (memcpy, memset), and buffer safety |
Launch Reader ↗ |
| Recursion Recipe (Tricks & Patterns) | Recursive call stack anatomy, base case formulation, divide-and-conquer strategies, and backtracking algorithms | Launch Reader ↗ |
JavaScript Notebooks
Comprehensive vanilla JavaScript curriculum spanning core semantics, browser APIs, DOM/BOM manipulation, and modern ES6+ features.
- Library Hub: sagarbiswas-multihat.github.io/javascript-notebooks
| Notebook | Focus & Core Topics | Live Reader |
|---|---|---|
| JSON (JavaScript Object Notation) | Data interchange formats, serializing and deserializing payloads, schema validation, and JSONPath querying | Launch Reader ↗ |
| Part 1 - JavaScript Basics | Language fundamentals: data types, variables (var, let, const), operators, control flow, functions, arrays, and objects |
Launch Reader ↗ |
| Part 2 - Web Storage API | Client-side persistence mechanics: localStorage vs sessionStorage, quota constraints, and security considerations |
Launch Reader ↗ |
| Part 3 - Document Object Model (DOM) | DOM tree traversal, querying elements, event bubbling and capturing, dynamic DOM mutation, and defensive DOM security | Launch Reader ↗ |
| Part 4 - Browser Object Model (BOM) | Browser environment APIs: the window, navigator, screen, location, and history objects, timers, and dialogs |
Launch Reader ↗ |
| Part 5 - Best Practices, Error Handling, and Canvas | Robust error handling (try/catch/finally), clean coding standards, and 2D pixel rendering using the HTML5 Canvas API |
Launch Reader ↗ |
| Part 6 - Modern ES6+ Essentials & Deep Dive | Arrow functions, destructuring assignment, spread/rest operators, Promises, async/await, and native ES modules |
Launch Reader ↗ |
React Notebooks
Modern component architecture, reactive state management, built-in hooks, and production application patterns.
- Library Hub: sagarbiswas-multihat.github.io/react-notebooks
| Notebook | Focus & Core Topics | Live Reader |
|---|---|---|
| Part 1 - Foundations (1 to 11) | Component design, JSX syntax rules, unidirectional data flow, props interfaces, and conditional rendering | Launch Reader ↗ |
| Part 2 - State + Hooks (12 to 24) | State management and side effects: useState, useEffect, useRef, useMemo, useCallback, and custom hooks |
Launch Reader ↗ |
| Part 3 - Forms + Todo Apps (25 to 30) | Controlled components, form state validation, event handling, CRUD architecture, and application state modeling | Launch Reader ↗ |
PHP Notebooks
Server-side web engineering, defensive input validation, database abstraction, sessions, and MVC architecture.
- Library Hub: sagarbiswas-multihat.github.io/php-notebooks
| Notebook | Focus & Core Topics | Live Reader |
|---|---|---|
| Part 1 - Introduction to PHP | Server runtime execution, syntax, superglobals ($_GET, $_POST, $_SERVER), arrays, and request lifecycles |
Launch Reader ↗ |
| Part 2 - HackProof PHP Form Validation | Defensive backend filtering, data sanitization, XSS mitigation, CSRF token validation, and secure submission handling | Launch Reader ↗ |
| Part 3 - PHP Sessions & Cookies | Session lifecycle management, session fixation defenses, and secure cookie configuration (HttpOnly, Secure, SameSite) |
Launch Reader ↗ |
| Part 4 - Data Access Using PHP | Database connectivity via PDO, prepared statements, parameterized queries, and SQL injection prevention | Launch Reader ↗ |
| Part 5 - PHP & MySQL Introduction | Relational database modeling, SQL queries, table joins, schema constraints, and dynamic record retrieval | Launch Reader ↗ |
| Part 6 - PHP MVC Handbook | Model-View-Controller design pattern, custom routing mechanisms, controllers, and clean separation of concerns | Launch Reader ↗ |
| Part 7 - AJAX & JSON | Asynchronous HTTP communication with backend scripts, REST-style endpoints, and JSON serialization | Launch Reader ↗ |
Bash Scripting Notebooks
Linux terminal automation, process orchestration, POSIX shell patterns, and administration scripts.
- Library Hub: sagarbiswas-multihat.github.io/bashscript-notebooks
| Notebook | Focus & Core Topics | Live Reader |
|---|---|---|
| Bash Scripting Notebook | Shell scripting, standard I/O streams, pipelines, conditionals, loops, functions, regex, and Linux task automation | Launch Reader ↗ |
Git & GitHub Notebooks
Distributed version control, branching topologies, team collaboration, and repository governance.
| Notebook | Focus & Core Topics | Live Reader |
|---|---|---|
| Git & GitHub Notebook (Part 1) | Version control fundamentals: commit trees, staging, branch workflows, merge vs rebase, conflict resolution, and remote sync | Launch Reader ↗ |
NestJS Notebooks
Scalable, enterprise-grade server-side architecture built with TypeScript and progressive design patterns.
- Library Hub: sagarbiswas-multihat.github.io/nestjs-notebooks
| Notebook | Focus & Core Topics | Live Reader |
|---|---|---|
| NestJS Notebook (Part 1) | Modular enterprise backend architecture, TypeScript decorators, controllers, providers, services, and dependency injection | Launch Reader ↗ |
HTML / Other Notebooks
Foundational web standards, semantic document structuring, modern web markup, and accessibility.
- Library Hub: sagarbiswas-multihat.github.io/other-notebooks
| Notebook | Focus & Core Topics | Live Reader |
|---|---|---|
| The Ultimate HTML Handbook | Semantic HTML5 structure, web accessibility (a11y) standards, form inputs, meta tags, and search engine optimization | Launch Reader ↗ |
Browse all field manuals → · Read the research transmissions →
Clearance
Verified credentials
**Certified Phishing Prevention Specialist (CPPS)** Track: Social Engineering Defense  **Certified Red Operations Certificate** Track: Adversarial Operations 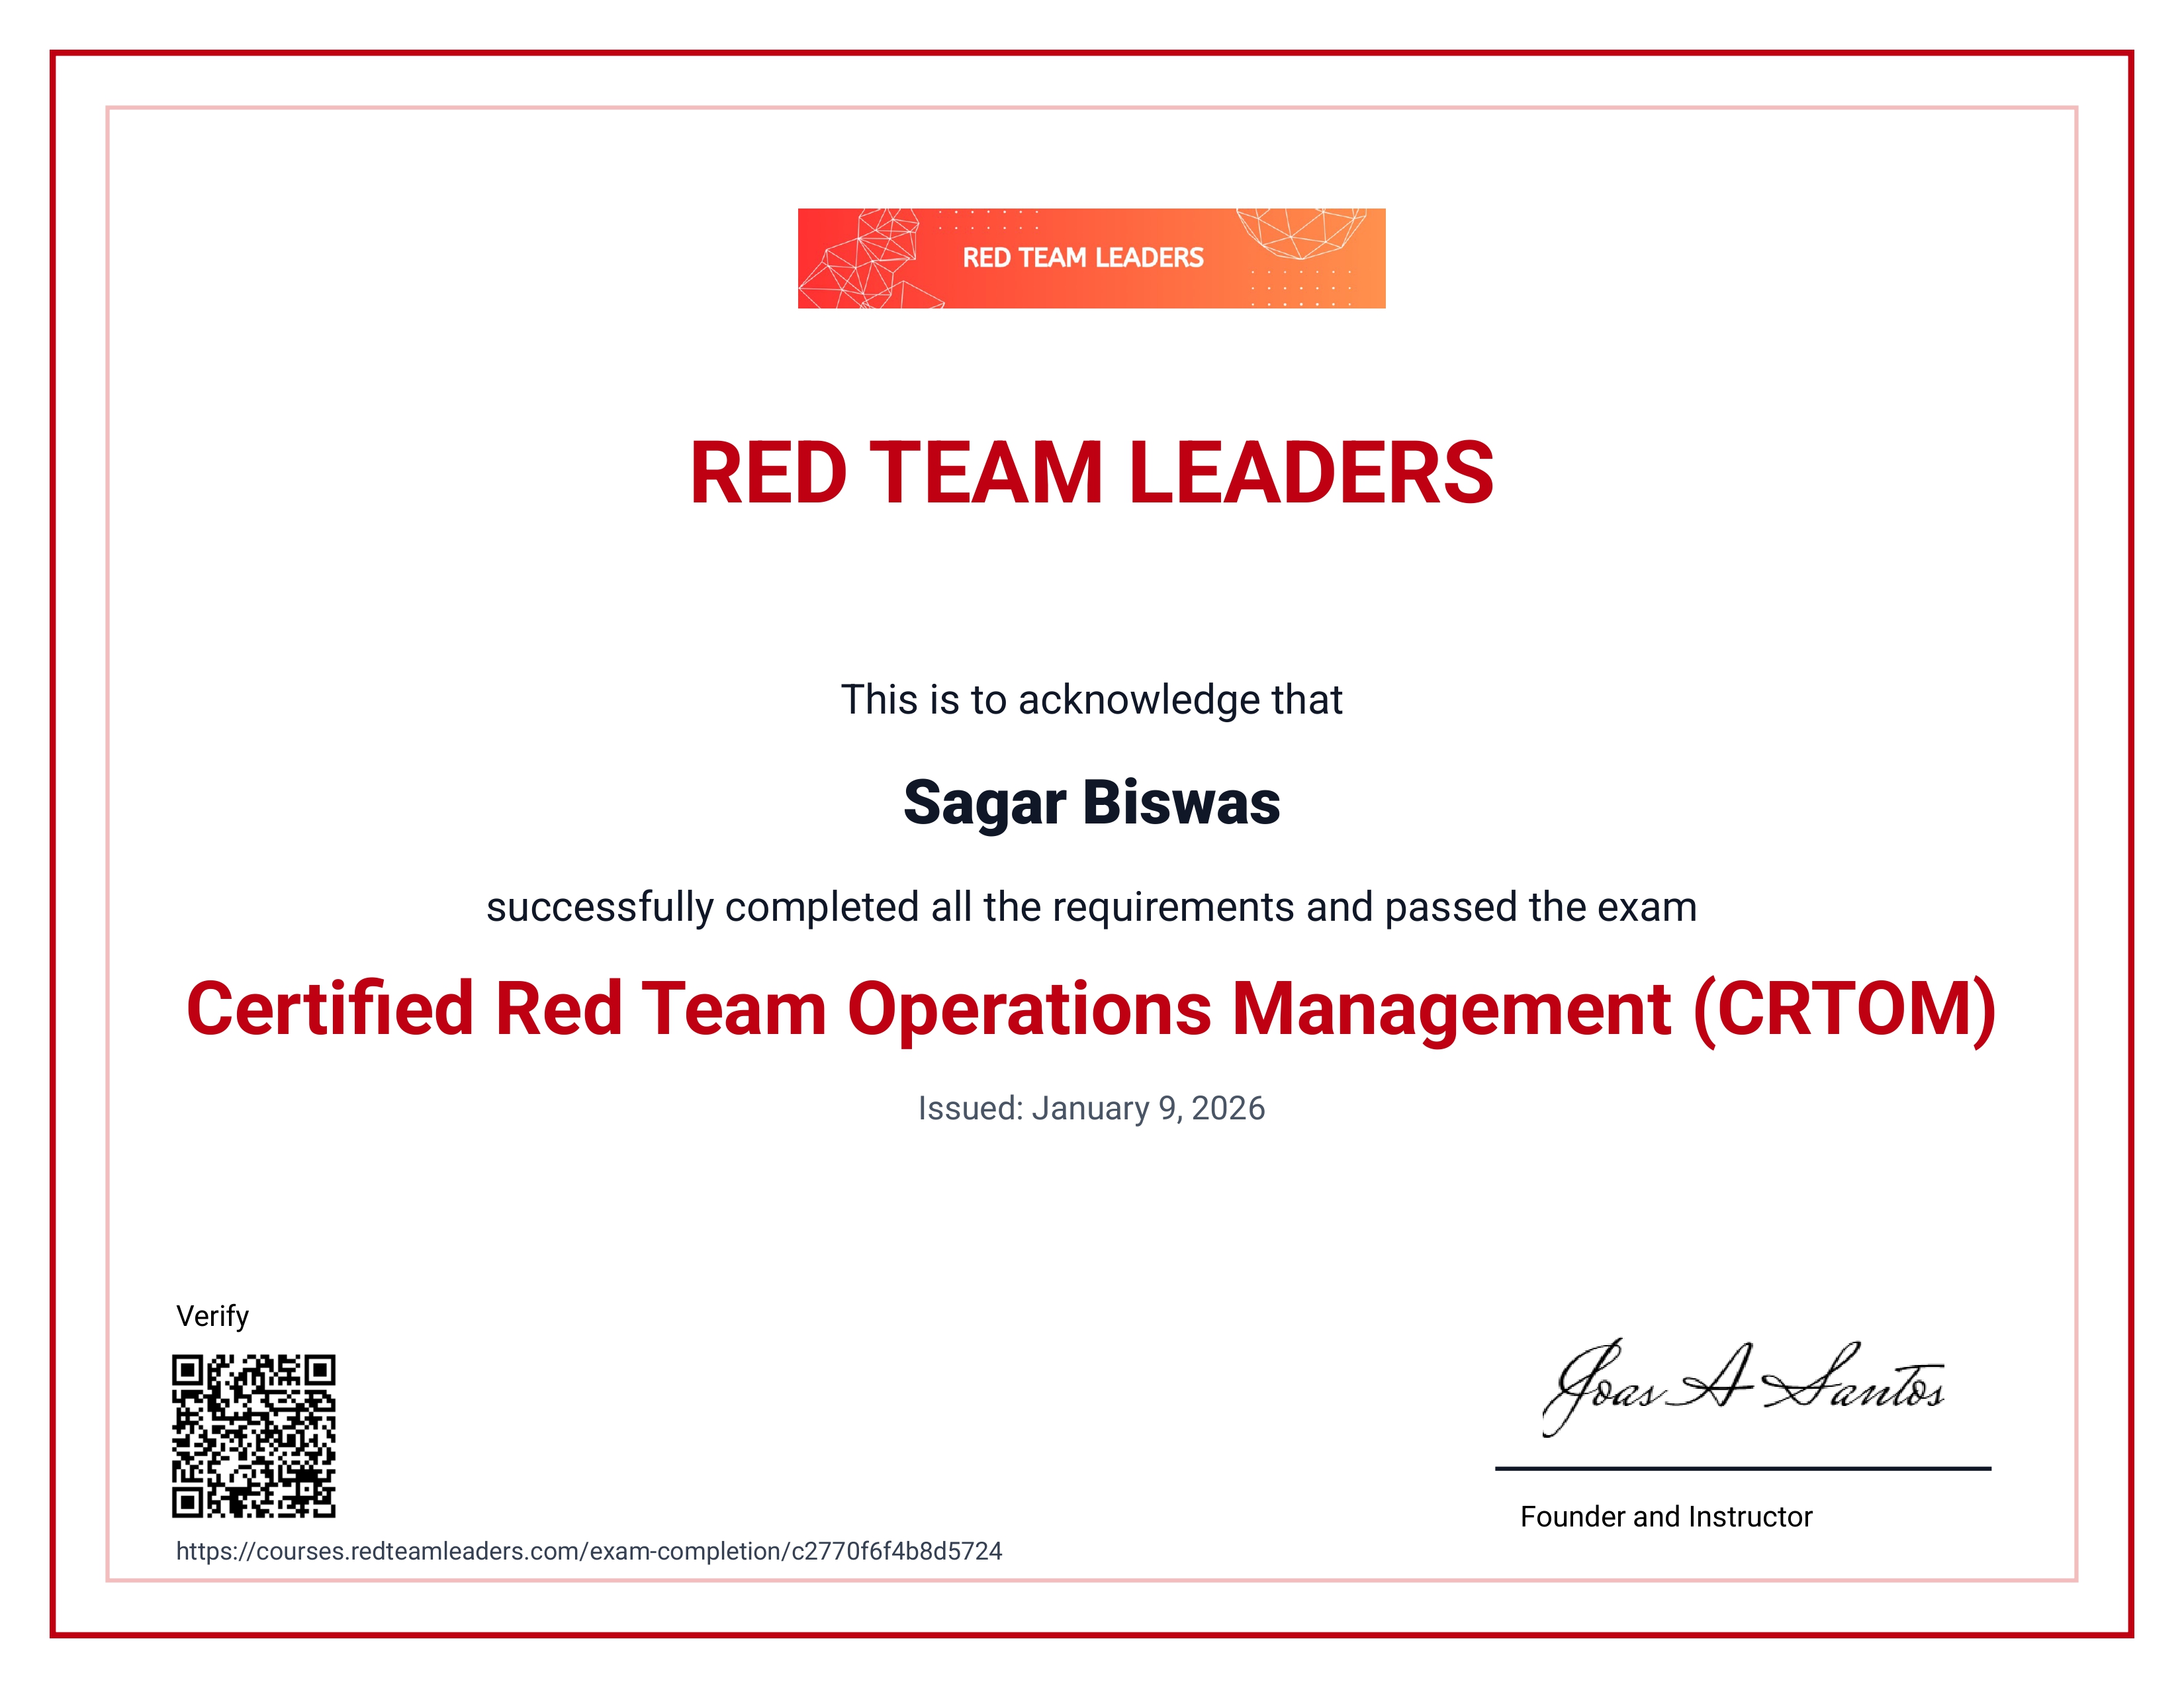 Full provenance and verification links: [Credential Vault →](https://sagarbiswas-multihat.github.io/certifications/)
Now
- Active: sharpening offensive/defensive web security instincts through PortSwigger Academy, TryHackMe, and Hack The Box
- Building: production systems in Next.js and NestJS under the MultiHAT banner
- Open to: open-source collaboration on cybersecurity and web-security tooling
- Ask me about: web app security, OSINT, Linux tooling, or the Next.js/NestJS stack
GitHub Analytics
Direct Channel


Founder-to-founder, recruiter, or fellow researcher: the fastest path in is email. For scope-defined security work, see the Responsible Disclosure note below.
Responsible Disclosure
If you find a security issue in any project here, report it privately first: sagarbiswas@multihat.dev or via Facebook, with enough detail to reproduce it. Please hold public exploit details until we’ve agreed on a remediation timeline (standard coordinated disclosure, nothing more).